Software development life cycle testing is the set of planned activities that helps teams find defects early, keep releases stable, and validate that software meets business goals. A comprehensive SDLC testing approach defines test objectives aligned to product requirements, implements layered test suites from unit to acceptance, and feeds results back into planning. Developers create and run unit tests, continuously integrating changes; testers design integration, system, and exploratory tests; managers track risk and prioritize fixes; and stakeholders use test evidence to accept releases. Properly scoped testing reduces rework, lowers long‑term cost, shortens time to detect regressions, and improves user satisfaction by preventing common production failures.
Key Takeaways
- Software development life cycle testing ensures defects are found early, maintaining stable releases and improving user satisfaction.
- Testing is essential at every SDLC phase – it validates requirements, confirms design, checks code, and supports regulatory compliance.
- Align test strategy and tools with each SDLC phase, ensuring coverage from unit to acceptance testing in production-like environments.
- Integrate automated tests into CI/CD pipelines to run on each commit, promoting fast feedback and continuous quality assurance.
- Avoid common pitfalls by testing early and often, maintaining test data hygiene, addressing flaky tests promptly, and including performance and security testing throughout development.
- Shared responsibility between developers and testers, along with periodic audits and clear quality goals, drives effective SDLC testing outcomes.
Why Testing Is Integral To The SDLC
Testing is not a final gate — it is a continuous activity that informs decisions across the SDLC. Early testing validates requirements (e.g., via acceptance criteria and examples), uncovers design mismatches during architecture and design reviews, and catches coding defects at the unit and integration levels. Test results create measurable signals for release readiness: pass/fail counts, severity distribution, and open defect trends. These signals influence scope decisions, prioritization of fixes, and go/no‑go decisions. Beyond functional correctness, testing verifies nonfunctional requirements — performance, scalability, security, and compliance — helping reduce post‑release incidents and support costs. When teams treat quality as a shared responsibility rather than a separate phase, they increase predictability, reduce technical debt, and maintain a reliable delivery cadence.
Testing Activities Mapped To Each SDLC Phase
Effective SDLC testing maps concrete activities to each phase so the right work happens at the right time. In the requirements phase, activities include defining clear acceptance criteria, creating example scenarios, and preparing traceability matrices. During design, teams perform design reviews, model‑based tests, and risk assessments to identify high‑impact areas requiring focused testing. In implementation, developers write unit and component tests and run static analysis; integration tests validate interfaces and data flows. In system and pre‑release phases, testers execute system, regression, performance, and security tests in production‑like environments, and product owners run acceptance testing. In release and maintenance, monitoring, synthetic transactions, and regression suites verify ongoing quality, while bug triage and root cause analysis feed improvements back into the backlog. Maintain traceability from requirement to test case and from test result to defect to ensure coverage and auditability.
Waterfall/Sequential Phase Testing: Roles, Deliverables, And Handoffs
In sequential or Waterfall models, testing activities and responsibilities are explicit at each handoff, which helps organizations with strict governance or regulatory needs. During requirements, test leads produce a test strategy and initial test plan. When design artifacts are delivered, teams derive test cases and define environments. Developers deliver code with unit tests; testers receive builds and execute system and acceptance tests according to the preapproved test plan. Testers log defects with reproduction steps and attach relevant artifacts; developers fix and provide patched builds for regression verification. Release managers coordinate regression runs and signoff checklists that include test coverage reports and open‑defect risk assessments. While this model emphasizes documentation and formal checkpoints, it benefits from adopting earlier testing activities (shift‑left) and automating regressions to reduce late surprises.
Best Practices For Effective SDLC Testing: Strategy, Tools, And Teamwork
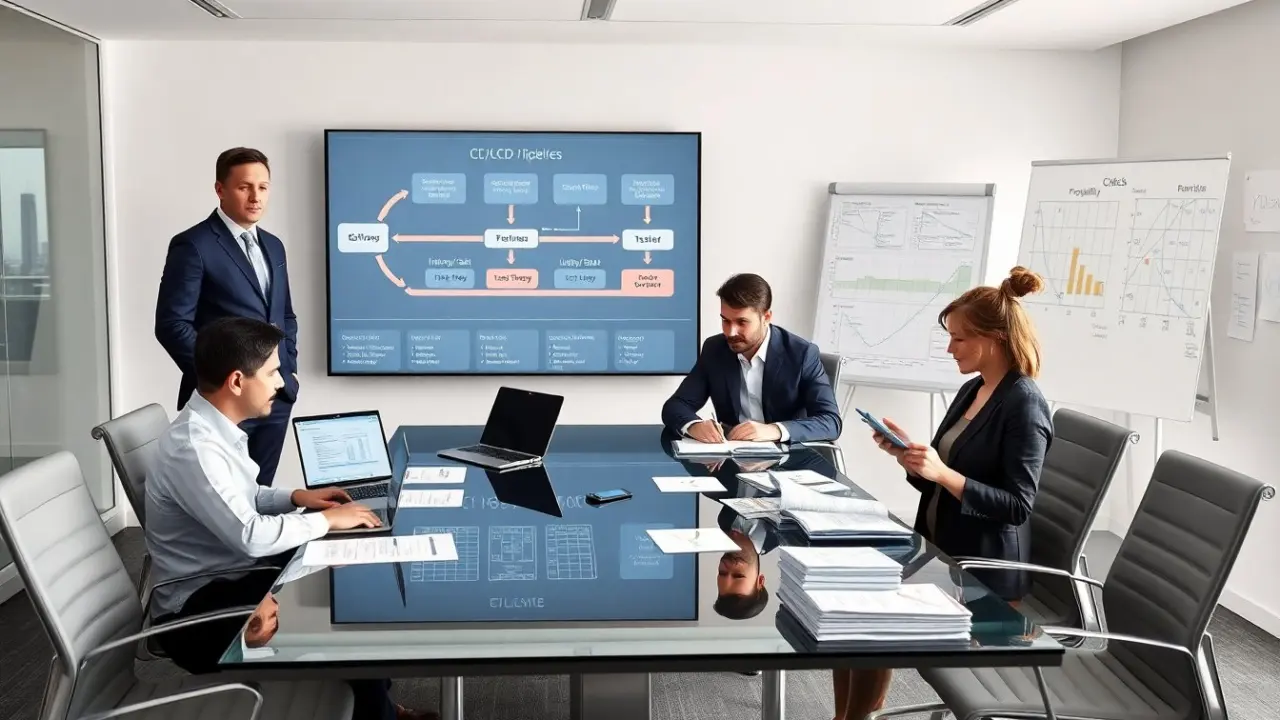
Start with a clear test strategy that ties to business risk and quality goals: define pass/fail criteria, determine test scope per release, and choose metrics to monitor (coverage, defect trend, build stability, test execution time). Select tools that match each level of testing — unit test frameworks and linters for developers, contract and integration test frameworks for services, UI automation for critical user journeys, and performance/security tooling for nonfunctional verification. Integrate tests into CI/CD pipelines so fast, automated checks run on each commit and longer suites run on scheduled gates. Maintain realistic, isolated test environments and curated test data that mirror production while protecting sensitive information. Encourage cross‑functional practices: pair developers and testers on story acceptance, use code reviews that include test validation, and run periodic test audits to identify gaps. Invest in flaky test management: triage failures, quarantine or fix flaky tests, and keep a clean baseline for confidence. Finally, make testing visible with dashboards and regular quality reviews so the team and stakeholders can act on results quickly.
Common Pitfalls And How To Avoid Them In SDLC Testing
Several recurring mistakes weaken SDLC testing; recognizing and preventing them improves outcomes. Common pitfalls include delaying testing until late stages (fix by shifting left and embedding test design in early sprints), relying exclusively on manual testing (address by automating repetitive, deterministic checks), and tolerating flaky tests (resolve by tracking flakiness metrics and remediating or removing unstable tests). Other issues are poor test data hygiene and environment drift (mitigate with versioned environment configurations and anonymized production‑like datasets), insufficient nonfunctional testing (include performance and security tests in pipelines and on preproduction mirrors), and weak traceability (maintain links from requirements to tests to defects). Adopt a risk‑based testing mindset: prioritize tests that reduce the most business risk, automate what is run frequently, and keep exploratory testing for areas requiring human judgment. Regular retrospectives on testing outcomes and a culture of shared ownership are the most effective long‑term defenses against these pitfalls.